Red Teaming Cybersecurity’s Elite Force for Proactive Defense
In the ever-evolving landscape of digital threats, organizations are constantly seeking innovative ways to bolster their defenses. While traditional security measures are essential, a more proactive and sophisticated approach is gaining significant traction: Red Teaming. Far from being a mere penetration test, Red Teaming is a strategic, simulated adversary operation designed to test the limits of an organization’s security posture, identify vulnerabilities that might otherwise go unnoticed, and ultimately, strengthen resilience against real-world attacks.
What Exactly is Red Teaming?
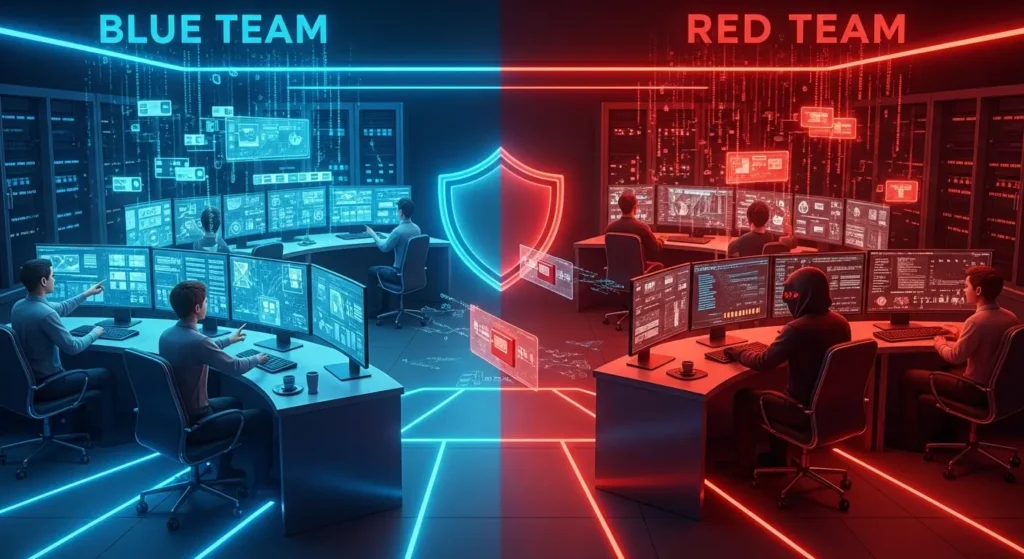
At its core, Red Teaming is a process where a dedicated team, known as the ‘Red Team,’ simulates the tactics, techniques, and procedures (TTPs) of actual threat actors. Their objective isn’t just to break into a system, but to achieve specific, pre-defined goals that mimic a real-world attack scenario. This could involve anything from stealing sensitive data, disrupting critical operations, or gaining persistent access to an organization’s network. Unlike a penetration test, which typically focuses on a specific system or vulnerability, Red Teaming adopts a broader, more holistic approach, considering all aspects of an organization’s defenses, including people, processes, and technology.
The ‘Blue Team’ and the ‘Red Team’ Dynamic
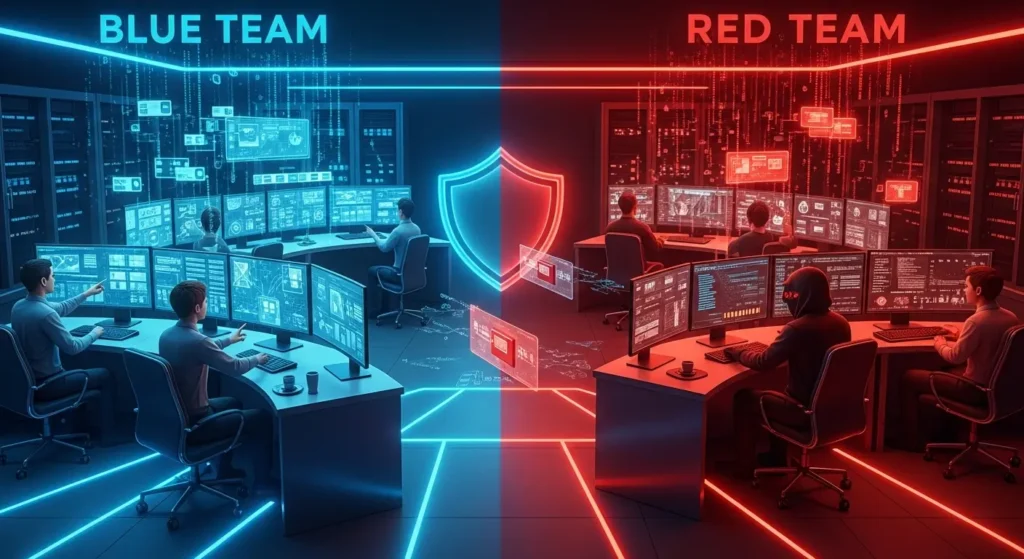
The Red Team operates in a controlled environment, with the knowledge that a ‘Blue Team’ – the organization’s internal security personnel – is actively monitoring and defending against their attacks. This adversarial relationship is crucial. The Red Team aims to bypass or defeat the Blue Team’s defenses, while the Blue Team strives to detect, respond to, and neutralize the Red Team’s activities. This dynamic mirrors real-world cyber warfare, providing invaluable insights into the effectiveness of an organization’s detection and response capabilities.
Why is Red Teaming So Crucial for Modern Businesses?
The digital realm is a battlefield, and threats are becoming increasingly sophisticated. Cybercriminals and state-sponsored actors are constantly developing new methods to breach defenses. Traditional security measures, while important, can sometimes create a false sense of security. Red Teaming offers a unique and invaluable perspective by:
- Uncovering Hidden Vulnerabilities: Red Teams go beyond superficial checks to discover complex, multi-stage vulnerabilities that might be missed by automated tools or standard penetration tests. They can exploit the ‘human element’ and the interconnectedness of systems to find weaknesses.
- Testing Real-World Attack Scenarios: Instead of theoretical exploits, Red Teaming simulates actual attack vectors used by malicious actors, providing a realistic assessment of how prepared an organization truly is.
- Evaluating Detection and Response Capabilities: A key outcome of Red Teaming is the assessment of how well the Blue Team can detect and respond to advanced threats. This helps identify gaps in monitoring, alerting, and incident response processes.
- Improving Security Awareness and Training: By observing how human elements are exploited, organizations can refine their security awareness training programs to better equip employees against social engineering and other human-centric attacks.
- Validating Security Investments: Red Teaming can help confirm whether the significant investments made in security technologies and personnel are actually effective in preventing and detecting sophisticated attacks.
- Enhancing Incident Response Plans: The lessons learned from Red Teaming exercises can directly inform and improve an organization’s incident response plans, making them more robust and actionable.
The Red Teaming Process: A Closer Look
A typical Red Teaming engagement involves several distinct phases:
1. Objective Definition and Scoping
This is the foundational stage where clear, measurable objectives are established. What specific goals should the Red Team aim to achieve? This might be gaining access to a specific server, exfiltrating a particular dataset, or disabling a critical service. The scope of the engagement is also defined, including the systems, networks, and personnel that will be involved.
2. Intelligence Gathering and Reconnaissance
The Red Team begins by gathering as much information as possible about the target organization, much like a real attacker would. This can involve open-source intelligence (OSINT) gathering from public websites, social media, and news articles, as well as more targeted reconnaissance activities.
3. Attack Planning and Execution
Based on the gathered intelligence, the Red Team devises a strategy and begins executing their attack plan. This phase involves a wide range of TTPs, including:
- Social Engineering: Phishing emails, pretexting calls, or even physical infiltration to gain access or information.
- Exploiting Vulnerabilities: Leveraging known or unknown (zero-day) vulnerabilities in software and hardware.
- Credential Stuffing and Brute-Force Attacks: Attempting to gain access using stolen or guessed credentials.
- Malware Deployment: Using custom or known malware to gain a foothold and move laterally within the network.
- Physical Security Testing: In some cases, Red Teams may test physical access controls.
4. Post-Exploitation and Objective Achievement
Once a foothold is established, the Red Team works to achieve their predefined objectives. This often involves privilege escalation, lateral movement across the network, and data exfiltration or system manipulation.
5. Reporting and Debriefing
The Red Team meticulously documents all their activities, findings, and the TTPs they employed. This information is then compiled into a comprehensive report, which is presented to the organization’s leadership and Blue Team. A thorough debriefing session allows for discussion of the findings, recommendations for remediation, and improvements to the security program.
Red Teaming vs. Penetration Testing: Key Differences
While often used interchangeably, Red Teaming and Penetration Testing are distinct. Penetration testing is typically more focused, aiming to identify vulnerabilities within a specific system or application within a defined timeframe. Red Teaming, on the other hand, is a more comprehensive, goal-oriented exercise that simulates a real adversary’s campaign over a longer period, testing the organization’s defenses holistically.

The Future of Cybersecurity: Embracing Proactive Defense
As cyber threats continue to evolve, the importance of Red Teaming will only grow. It’s no longer sufficient to simply react to breaches. Organizations must adopt a proactive stance, constantly challenging their own defenses to stay ahead of sophisticated adversaries. Red Teaming provides the critical insights needed to build truly resilient security programs, ensuring that businesses can navigate the digital landscape with confidence and security.